Secure Web Applications & DevSecOps
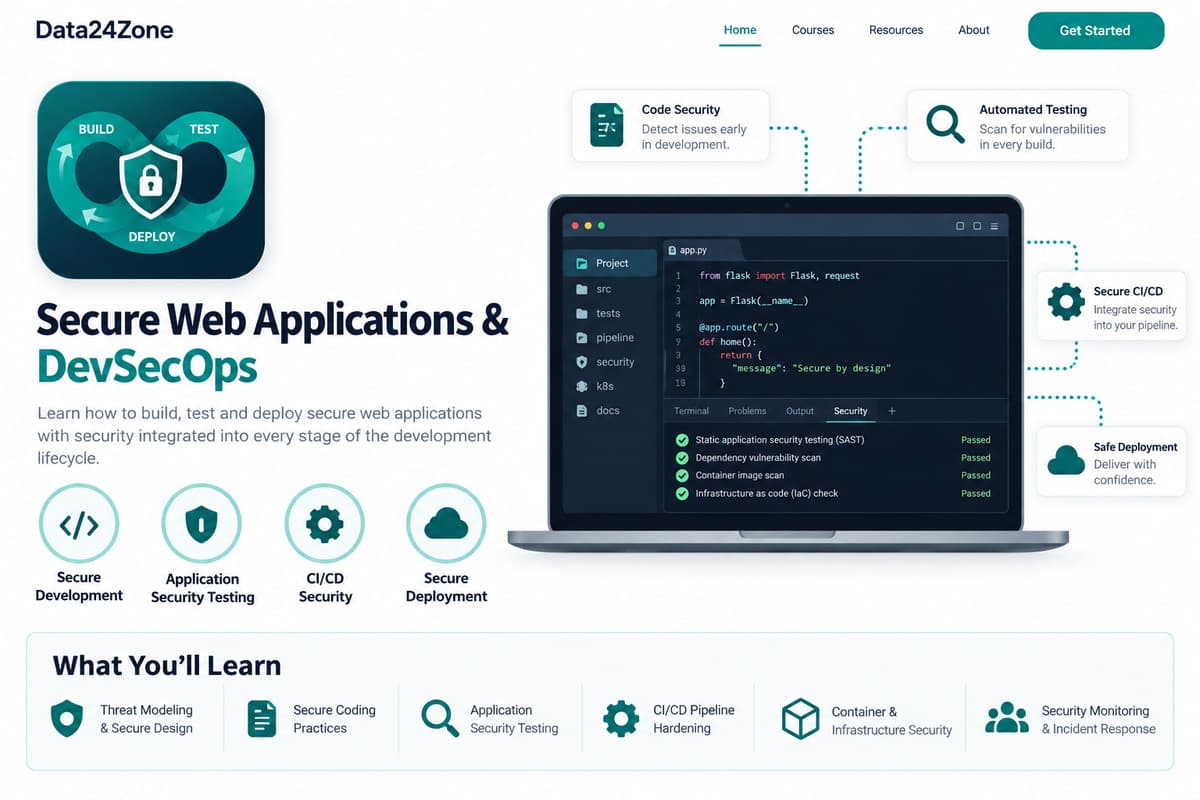
Secure Web Applications & DevSecOps is a 9-week intermediate course covering the OWASP Top 10, input validation, session security, secrets management, automated SAST/DAST scanning, supply-chain security, and threat modeling. Learners with backend API experience harden a small API against common vulnerabilities and deliver a threat-modeled, security-hardened course API with a CI security check and regression tests.
Build and test security controls at application boundaries and carry them through a controlled delivery process.
What you'll learn
Course details
Duration
9 weeks
Best for
Learners who already have: Backend APIs, authentication and basic deployment.
Enrollment isn't open for this course yet — check back soon or contact us.
Course Curriculum
A module-by-module breakdown of what you'll cover in Secure Web Applications & DevSecOps.
01Basic
4 topicsWeeks 1–2
- What Is DevSecOps, and Why "Shift Left" on Security?
- The OWASP Top 10: A Baseline Map of Common Web Vulnerabilities
- Input Validation and Parameterized Data Access
- Project: Security-Review a Small API and Add a CI Security Check
02Intermediate
4 topicsWeeks 3–4
- Session Security: Cookies, Tokens, and Secure Session Lifecycle
- Defending Against XSS and CSRF
- Secrets Management: Never Hardcoding Credentials
- Project: Harden Session Security, Prevent XSS/CSRF, and Audit Secrets
03Advanced
9 topicsWeek 5
- Turn a business request into a testable contract
- Enforce ownership and roles on the server
- Validate meaning and use parameterized data access
- Treat session lifecycle and browser protections as a system
- Review dependencies and release inputs as part of the boundary
- Test outcomes at the boundary where they can fail
- Keep untrusted workflow input away from privileged execution
- Connect logs, metrics and traces to a user outcome
- Package a reproducible release and a recovery path
04Pro
4 topicsWeeks 6–7
- Automated Security Scanning in CI/CD: SAST and DAST
- Supply Chain Security: SBOMs and Dependency Pinning
- Threat Modeling: Thinking Like an Attacker Before They Do
- Project: Threat Model a Feature, Then Harden Its Pipeline
05AI Pro
3 topicsWeeks 8–9
- Using Claude, ChatGPT, and Perplexity for Security Code Review and Threat Modeling
- Verifying AI-Assisted Security Reviews Before Trusting Them
- Project: AI-Assisted Threat Modeling and Security Review with Cross-Verification
Real-Time, Industry-Based Projects
This is project-based learning modeled on real industry scenarios — you'll build portfolio-ready work as you go, not just watch lectures.
Every course includes a guided internship on top of your project work — so you graduate with real experience, not just a certificate.
Communication & Soft Skills
Built into every course, alongside the technical curriculum.
Communication Skills
Practice explaining technical work clearly to teammates, managers, and clients.
Practical AI Skills
Hands-on training in using AI tools well — prompting, everyday workflows, and where AI actually helps versus where it doesn't.
Teamwork & Collaboration
Work in small project teams using real workflows like stand-ups and code reviews.
Problem Solving
Build the habit of breaking down ambiguous problems into clear, solvable steps.
Time Management
Learn to plan, prioritize, and deliver project work against realistic deadlines.
Presentation Skills
Present your project work and results with confidence, as you would to a client.
Resume & Profile Building
Build a strong resume, LinkedIn profile, and project portfolio that recruiters notice.
Interview Preparation
Mock interviews and portfolio reviews to get you ready for real job applications.
Career & Placement Support
100% of students enrolled in Secure Web Applications & DevSecOps get full access to placement support — real tools and guidance, not just a promise. This is support and access, not a guaranteed job outcome.
Resume Builder
A resume auto-built from your real completed projects and certificates, ready to export.
Shareable Portfolio
A public portfolio page showcasing your approved projects, with a link you can share with employers.
Interview Preparation
Guidance on presenting your projects and experience clearly in real interviews.
Peer & Mentor Community
Ongoing access to our learner community for questions, feedback, and support after you finish.
What Your Certificates Look Like
Real, verifiable certificates with your name, Secure Web Applications & DevSecOps, and a QR code anyone can scan to confirm they're genuine — one for completing the course, and a separate one if you take the internship track. Earning a certificate is free. To view, download and share it, there's a one-time ₹100 release fee per certificate — the same for free-course, paid-course and internship certificates.
Course Completion Certificate

 Data24Zone
Certificate of Completion
Illustrative recipient
Your Name Here
Example certificate for completion of
Secure Web Applications & DevSecOps
- Certificate No.
- D24-SAMPLE
- Mode
- Self-Paced
- Duration
- 9 weeks
- Example issue date
- On completion
Sample only — not a real, issued certificate.
Verification is available only on issued certificates.
Internship Completion Certificate
Data24ZoneCertificate of Internship
Illustrative recipient
Your Name Here
Example certificate for completion of
Secure Web Applications & DevSecOps
- Certificate No.
- D24-SAMPLE
- Mode
- Internship
- Duration
- 9 weeks
- Example issue date
- On completion
Sample only — not a real, issued certificate.
Verification is available only on issued certificates.
Frequently Asked Questions
What will I learn in the Secure Web Applications & DevSecOps course?
You'll learn: Turn a business request into a testable contract; Enforce ownership and roles on the server; Validate meaning and use parameterized data access; Treat session lifecycle and browser protections as a system.
Is the Secure Web Applications & DevSecOps course beginner-friendly?
This is a intermediate-level course, so it assumes some prior familiarity with the subject.
How long does the Secure Web Applications & DevSecOps course take to complete?
The course is designed to be completed in approximately 9 weeks, depending on your pace.
What enrollment options are available for Secure Web Applications & DevSecOps?
Project Training Track (₹1,499) — One defined learning project and 2 review sessions; no employment or stipend included. Self-Paced (₹1,999) — Learn anytime with the full recorded curriculum and community access.
Is there an internship option for Secure Web Applications & DevSecOps?
Yes — the Internship track means working through real projects with our team and earning a separate Internship Certificate.
Will I get a certificate after completing Secure Web Applications & DevSecOps?
Yes. Self-paced enrollment earns a course completion certificate once your final project is reviewed and approved. Internship enrollment earns an internship certificate once your internship projects are approved. Every certificate is publicly verifiable on our website and can be added directly to your LinkedIn profile. Earning it is free; releasing it to view, download and share is a one-time ₹100 fee per certificate.
What kind of projects will I build in Secure Web Applications & DevSecOps?
You'll work on real projects such as: Security-hardened course API with a threat model and regression tests.
Is placement support included with Secure Web Applications & DevSecOps?
Yes — every enrolled student gets full access to our placement support: resume building, a shareable project portfolio, mock interview preparation, and guidance applying what you've built to real job applications. This is support and access, not a guaranteed job outcome — how quickly it leads to an offer depends on the market and your own effort.